Skip to content

GRCIAMSAP Security Governance

Get a grip on access, risks and compliance

I’m Virgil Verloop, an independent consultant since 2008. For almost twenty years I have helped organisations get a grip on who may do what, on their risks and on the evidence that they are in control. From analysis and vision, through requirements and tool selection, to implementation, adoption and training.

Clients include

  • Vitens
  • PostNL
  • NS
  • ABN AMRO
  • Alliander
  • Agrifirm
  • ProRail
  • ASML
  • Philips
  • ING

My motto

Secure business-critical processes and systems by using people, transparency and automation to break down the silos and allow connection.

What I do

What do you want a firmer grip on?

Five areas where I give organisations a grip, as a consultant, product owner or project manager. Always with the same approach: make visible what is there, bring structure, bring people together and set up the governance that keeps it in place.

Grip on who may do what

Identity & Access Management

Identity lifecycle management that moves with HR: joiners, movers and leavers provisioned automatically from the source system to SAP, Microsoft and other systems, including the manual ones. From architecture and tool selection to a working, end-to-end tested IAM chain.

For example: at Vitens I defined the IAM and GRC architecture; linking HR job functions to GRC business roles delivered 80% automated provisioning (SAPinsider, 2019).

  • Microsoft Entra ID Governance
  • SailPoint
  • SAP Cloud Identity Services
  • SAP IAG

Grip on risks and assurance

Governance, Risk & Compliance

The complete GRC journey: from analysis and vision, through requirements and tool selection, to implementation, adoption and training. Certified in SAP GRC Access Control, experienced with releases 10.0 through 12.0 and with IAG in the cloud: risk analysis, access requests with an upfront risk check, SoD rulesets and Firefighter.

For example: at PostNL I built the company-wide SoD ruleset in workshops with process owners, Audit, Internal Control and IT, and led the SAP GRC 10.0 project for central emergency access.

  • SAP GRC Access Control
  • SAP IAG
  • SoD ruleset
  • Firefighter
  • GRC100 trainer

Grip on threats and vulnerabilities

SAP Cybersecurity

Hardening SAP landscapes against current threats: tracking vulnerabilities and patches and detecting threats. With SecurityBridge as the platform for vulnerability management, patch management and threat detection, and a feasibility study or pilot before you invest.

For example: at Vitens I implemented SecurityBridge and, together with KPMG, developed the ITGC framework with mitigating controls for the thirty most important risks.

  • SecurityBridge
  • Patch management
  • Threat detection
  • Hardening
  • ITGC

Grip on business risks

Enterprise Risk Management

From access risks to the broader risk and control framework: risk ownership in the business, monitoring in the second line and a reliable audit trail for the third line, following the Three Lines Model. And where it fits: the step to SAP Process Control and Risk Management.

For example: at Vitens I embedded purchase-to-pay in the Three Lines Model and wrote the business case for SAP Process Control as the extension towards enterprise GRC.

  • Three Lines Model
  • SAP Process Control
  • COBIT
  • GRCP (OCEG)

Grip on roles and segregation of duties

SAP Authorisations

Authorisation concepts and role models that deliver least privilege and stay auditable: job-based roles, a risk ruleset and structurally cleaning up SoD conflicts. Also for S/4HANA, SAP Datasphere, SAP Analytics Cloud and BTP.

For example: at Bilthoven Biologicals I implemented a new authorisation concept with a risk ruleset, including GxP processes, through to go-live.

  • Role design
  • SoD analysis
  • S/4HANA
  • Datasphere and SAC
  • BTP

Not sure where to start?

The maturity scan shows where you stand and what to tackle first.

About the scan

Start small

IAM and GRC maturity scan

A compact first step. I assess how mature your organisation is in identity & access management and/or GRC: policy, organisation, processes and technology against a maturity model, complemented by conversations with the key stakeholders.

Request the scan

What I assess

  • Policy
  • Organisation
  • Processes
  • Technology

What you get

  1. A clear picture of where you stand
  2. A roadmap for the coming years
  3. Quick wins for the first quarter

Assignments

In practice

Full overview on LinkedIn

2015 – present

Vitens

Product Owner and Solution Architect IAM, SAP Security and GRC

  • Implemented SAP GRC Access Control, IAG and SAP Cloud Identity Services
  • Implemented SecurityBridge for vulnerabilities, patches and threat detection
  • Embedded purchase-to-pay in the Three Lines Model

2024 – 2025

Alliander

GRC lead consultant, tool selection and roadmap

  • Requirements that validated SailPoint as the GRC solution
  • Three-year roadmap drawn up within the IAM programme

2022 – 2024

NS

SAP GRC consultant

  • Reviewed the GRC setup and executed the improvement plan with the team
  • Trained the team to continue independently with GRC

2009 – 2015

PostNL

Lead consultant, project manager and team lead SAP Security

  • Company-wide SoD ruleset built in workshops with process owners, Audit, Internal Control and IT
  • Project manager of the SAP GRC 10.0 project for central emergency access (Firefighter)

Approach

How I work

Whether it is a scan, a roadmap or an implementation, the approach is always the same.

  1. Make it transparent

    First see what is there: who has which access, where the risks are, how processes really run and who is accountable for what. Based on data, not assumptions.

  2. Bring structure

    A clear model of roles, ownership and processes, and a roadmap that everyone understands and can execute step by step.

  3. Bring people together

    Business, IT, audit, internal control and security at one table. That is where decisions are made that last, and where support grows.

  4. Set up governance

    Ownership, controls, monitoring and an audit trail, with automation where possible. So it keeps working after the project ends: get clean, stay clean, stay in control.

Publications and speaking

Knowledge sharing

  • Speaker at TAC

    Amsterdam, March 2026: Best-of-Breed Approach for Identity Governance and SAP Security in a Hybrid Cloud Landscape, the Vitens approachSlides (pdf)Video (YouTube)

    May 2023: SAP GRC & IAM @Vitens, Access Control in a hybrid SAP and non-SAP landscape with IAG as the bridge, together with Hendrik Bijma (Vitens)Slides (pdf)Video (YouTube)

  • SAPinsider

    Customer case (2019): Drinking Water Company Vitens Connects HR and GRC Business Roles to Achieve an 80% Automated Provisioning RateRead the case (pdf)On sapinsider.org

    SAPinsider GRC 2019, Amsterdam and Barcelona: How Vitens maximizes SAP GRC 12.0 in a SAP and non-SAP landscape, together with Tinette Beuving (Vitens)Slides (pdf)

  • VNSG Magazine

    Cover story (February 2023) on the GRC and IAM transformation at Vitens, online on the VNSG blog, in DutchRead the online version

  • VNSG events

    Security Theme Day 2023, Baarn: Hoe koppel je SuccessFactors aan GRC Access Control via Cloud Integration om joiners, movers en leavers te automatiseren (connecting SuccessFactors to GRC Access Control via Cloud Integration to automate joiners, movers and leavers), together with Hayo Cnossen (Agrifirm), in DutchSlides (pdf)

    2011: SAP GRC 10.0 Access Control, Central Emergency Access at PostNL, together with Bernd Mobach (PostNL), in DutchSlides (pdf)

  • Book

    Co-author of Information Risk Management in de praktijk (in Dutch)View on bol.com

  • Trainer

    SAP GRC and IAG, including the GRC100 curriculum (Access Control, Process Control and Risk Management)

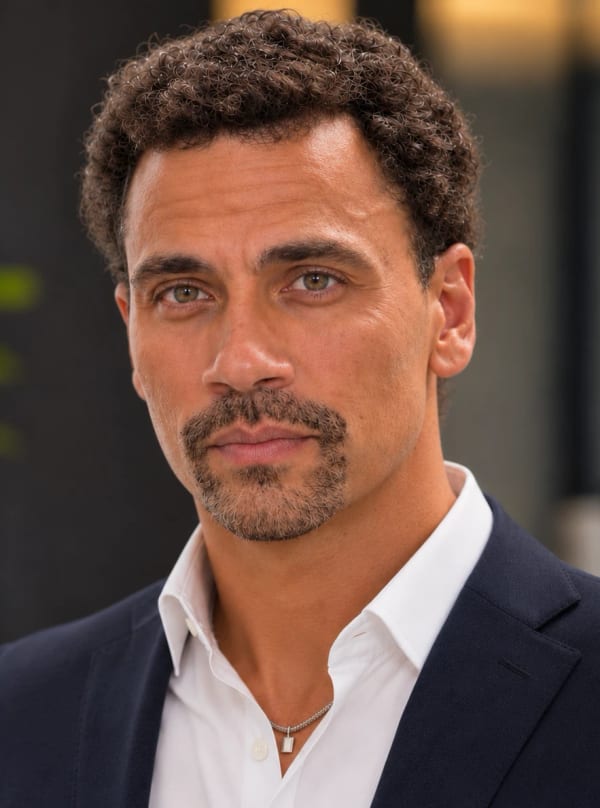
Portrait of Virgil Verloop

About Virgil

As comfortable in the boardroom as in the configuration

Previously a consultant at Atos Consulting (2005–2008), independent with Profilus since 2008. I work as a consultant, product owner or project manager: from strategy and architecture to implementation and operations. A connector: analytical, results-driven and equally at ease with the business and with IT operations.

Certified

CISA · CISSP · GRCP · SAP GRC Access Control

Contact

Start with a conversation

Tell me what you want a firmer grip on. Then we’ll work out the first step together.